
CERT-In’s six-hour rule, explained for CA firms
Since 2022, a serious cyber incident must be reported to CERT-In within six hours of noticing it. Who it applies to, what counts, how to report, and the log and clock duties that come with…
Since 2022, a serious cyber incident must be reported to CERT-In within six hours of noticing it. Who it applies to, what counts, how to report, and the log and clock duties that come with…
How to confirm your office server is sending spam, how to stop it, and what Indian law says about your responsibility: CERT-In’s six-hour report, IT Act section 43A today and the DPDP Act from May…
What to do, in order, when your office server is hacked: contain it without switching it off, report to CERT-In within six hours, recover, and tell the people who need to know. Written for Indian…
Seven signs that an attacker may already be on your Windows server, the event ID or check for each, and what to do in the first hours, including the CERT-In report.
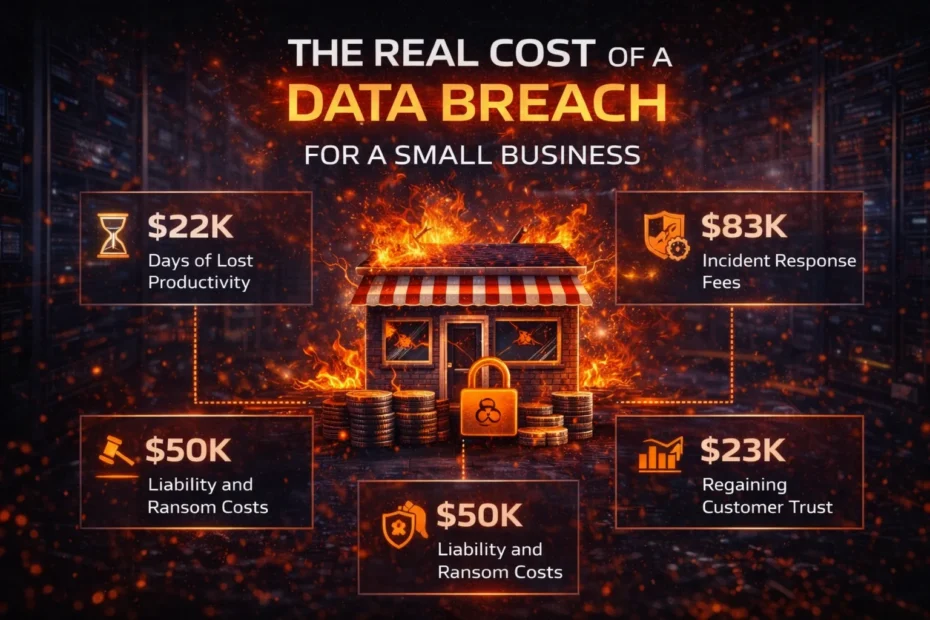
What a breach really costs a small Indian firm: downtime in tax season, client confidentiality, CERT-In and DPDP penalties, and why the ransom is a poor bet. With IBM’s India figures and a way to…
How ransomware gets into a small firm’s Windows server through RDP, phishing, weak passwords and missing patches, what happens before the ransom note, and what kind of backup actually survives.