
How to Change Your RDP Port (and Why It Is Not Enough)
How to change the Remote Desktop port on Windows Server safely, with PowerShell and a scoped firewall rule, and why a new port only cuts log noise rather than stopping attacks.
How to change the Remote Desktop port on Windows Server safely, with PowerShell and a scoped firewall rule, and why a new port only cuts log noise rather than stopping attacks.
Five steps to secure a small office’s Windows server in an afternoon: take Remote Desktop off the internet, set account policies, patch, cut admin access and watch the logs.
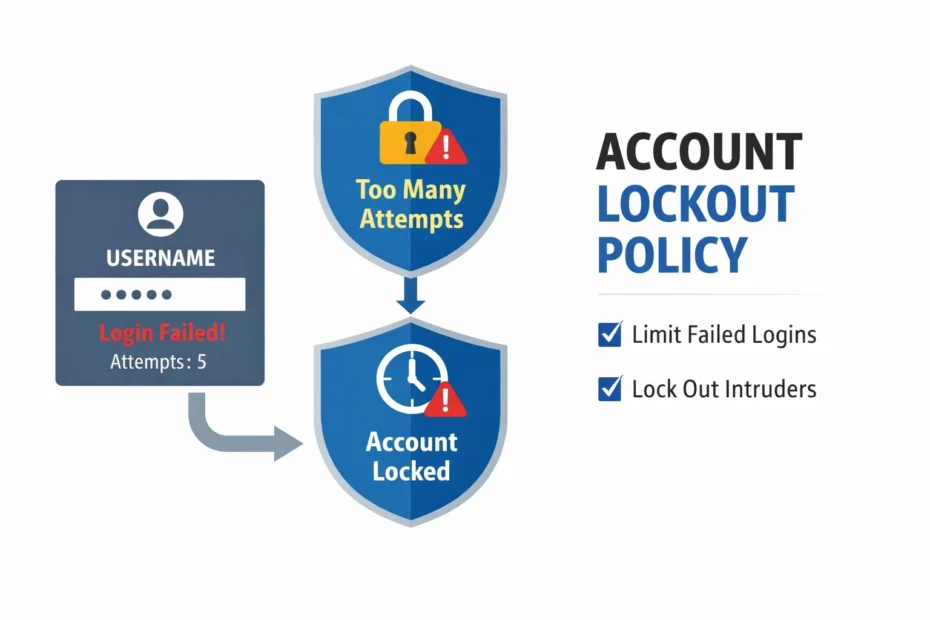
What an account lockout policy does on Windows, Microsoft’s 10/10/10 defaults, the built-in Administrator gap, how to set it up in five minutes, and where lockout falls short.
How to confirm your office server is sending spam, how to stop it, and what Indian law says about your responsibility: CERT-In’s six-hour report, IT Act section 43A today and the DPDP Act from May…
Network Level Authentication makes Remote Desktop users prove who they are before Windows starts a session. What it protects against, what it does not, and how to switch it on.
Credential stuffing turns one leaked password into a key for your email, tax portals and office server. How it works, what reuse looks like in a CA office, and how to stop it.
What to do, in order, when your office server is hacked: contain it without switching it off, report to CERT-In within six hours, recover, and tell the people who need to know. Written for Indian…
Seven signs that an attacker may already be on your Windows server, the event ID or check for each, and what to do in the first hours, including the CERT-In report.
A fifteen-minute check of your Windows Server firewall: are all three profiles on, which risky ports are open to anyone, and what your router is forwarding to the server.

The event IDs that show an attack in progress on a Windows server (4625, 4740, 4624, 4720, 4732, 7045, 1102), how to check them in a minute, and what to do next.